> ## Documentation Index
> Fetch the complete documentation index at: https://docs.requestly.com/llms.txt
> Use this file to discover all available pages before exploring further.
# Hawk
> Sign requests with a Hawk message authentication code.
Hawk signs each request with a message authentication code computed from a shared key. The key itself never leaves your machine, and the signature covers the method, the URI, the host, the port, and optionally the request body, so a replayed or tampered request fails verification.
Requestly builds the `Authorization: Hawk` header on every send. You supply the ID and the key; the nonce and the timestamp can be left to Requestly.
Hawk is offered for HTTP, GraphQL, WebSocket and Socket.IO requests. It is not offered for gRPC.
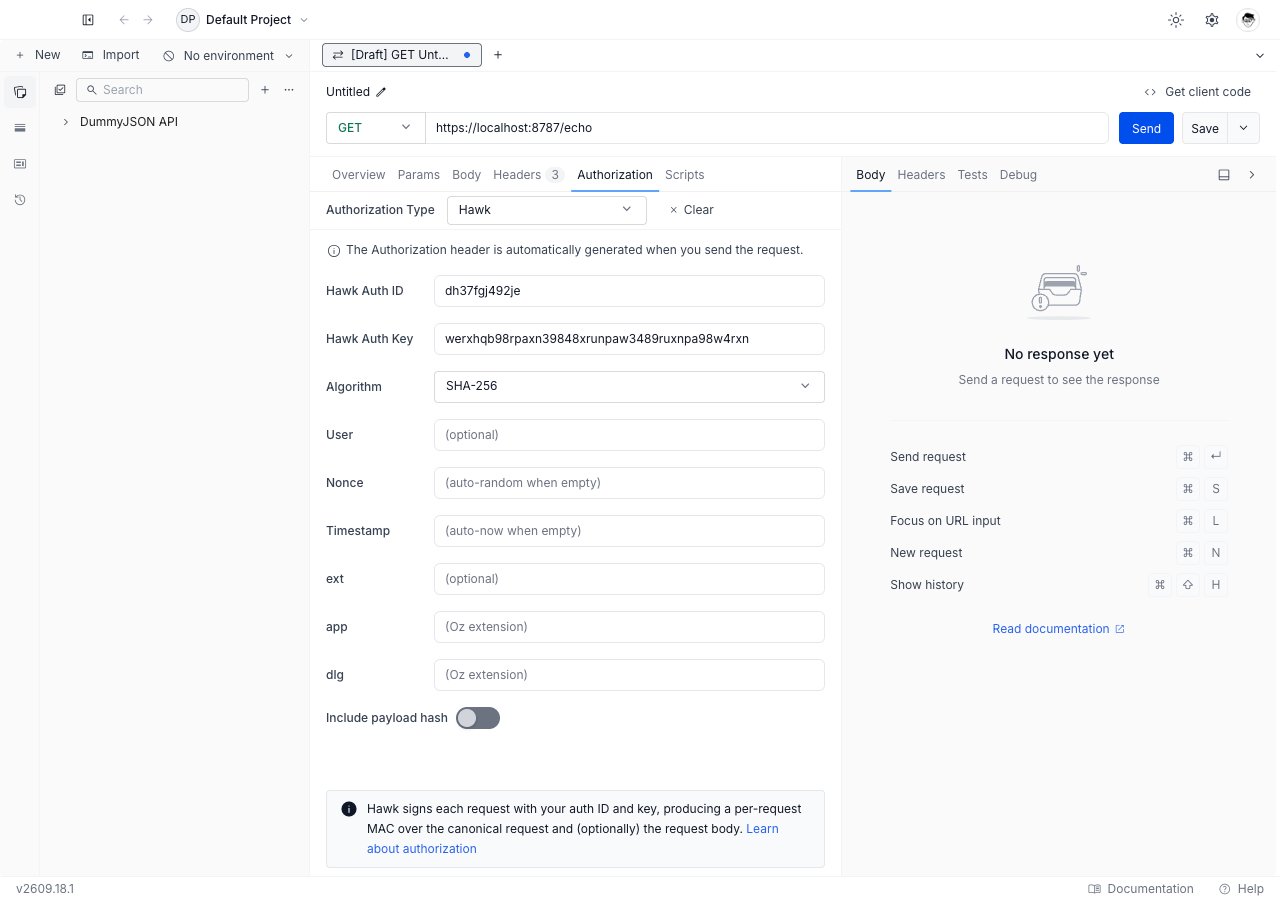
 ## Set up Hawk
Open any request or collection, then go to the **Authorization** tab.
Pick **Hawk** from the **Authorization Type** dropdown. The Hawk fields appear below the dropdown.
Fill in **Hawk Auth ID** and **Hawk Auth Key**. These are the credential pair the API gave you; everything else is optional.
Leave **Algorithm** on `SHA-256` unless the API specifies `SHA-1`. The two sides must agree or verification fails.
Click **Send**. Requestly computes the MAC and attaches the `Authorization: Hawk` header.
## Field reference
### Required
| Field | Purpose |
| ----------------- | --------------------------------------------------------------------------------- |
| **Hawk Auth ID** | The public identifier for your credential pair. Travels on the wire as `id`. |
| **Hawk Auth Key** | The shared secret used to compute the MAC. Never sent; only the resulting MAC is. |
| **Algorithm** | `SHA-256` (default) or `SHA-1`. Must match what the server expects. |
Both credential fields accept Requestly [variables](../../environments-and-variables) and [vault](../../vault/vault) references. Store the key as a vault secret and reference it as `{{vault:hawk_key}}`.
### Optional
| Field | Purpose |
| ------------- | ------------------------------------------------------------------------------------------------ |
| **User** | A local label for your own reference. Requestly does not send it, and it is not part of the MAC. |
| **Nonce** | A unique value per request. Leave blank and Requestly generates a random one on every send. |
| **Timestamp** | Unix time in seconds. Leave blank and Requestly uses the current time on every send. |
| **ext** | Free-form application data. It is bound into the MAC and echoed in the header as `ext`. |
| **app** | Application ID, from the Oz extension to Hawk. |
| **dlg** | Delegated-by application ID, also from Oz. It is only sent when **app** is also set. |
Leave **Nonce** and **Timestamp** blank. A fresh nonce and a current timestamp are what stop a captured request from being replayed, and Requestly produces both for you.
### Include payload hash
When this is on, Requestly hashes the request body and binds the result into the MAC, so the signature covers the body as well as the request line. Turn it on when the API validates payload integrity, and leave it off otherwise. A server that does not expect a payload hash will reject the request when one is present.
## Inherit Hawk from a collection
Set Hawk once on the collection and leave every request inside it on **Inherit from parent**. Requestly walks up from the request to the nearest ancestor that sets a concrete auth type and signs with that credential pair. The nonce and timestamp are still generated per request, so inheriting one configuration does not reuse one signature.
A request that picks its own auth type stops inheriting, and a collection or folder whose auth type is cleared or left unset stops the walk for everything below it.
## Troubleshooting
Check the algorithm first: a `SHA-256` signature against a `SHA-1` verifier always fails. Then check that the key was pasted without a trailing newline, and that your machine clock is accurate, since most Hawk servers reject timestamps more than a minute or two out.
Turn **Include payload hash** off, or turn it on, depending on which side you changed. Both ends must agree on whether the body is part of the signature.
`dlg` only travels when `app` is also set. Fill in **app** as well.
## What's Next?
The other per-request signing scheme in the dropdown.
Keep the Hawk key out of the collection.
Back to every auth type Requestly supports.