NTLM authentication requires the desktop app. Download Requestly.
Set up NTLM
1
Open the Authorization tab
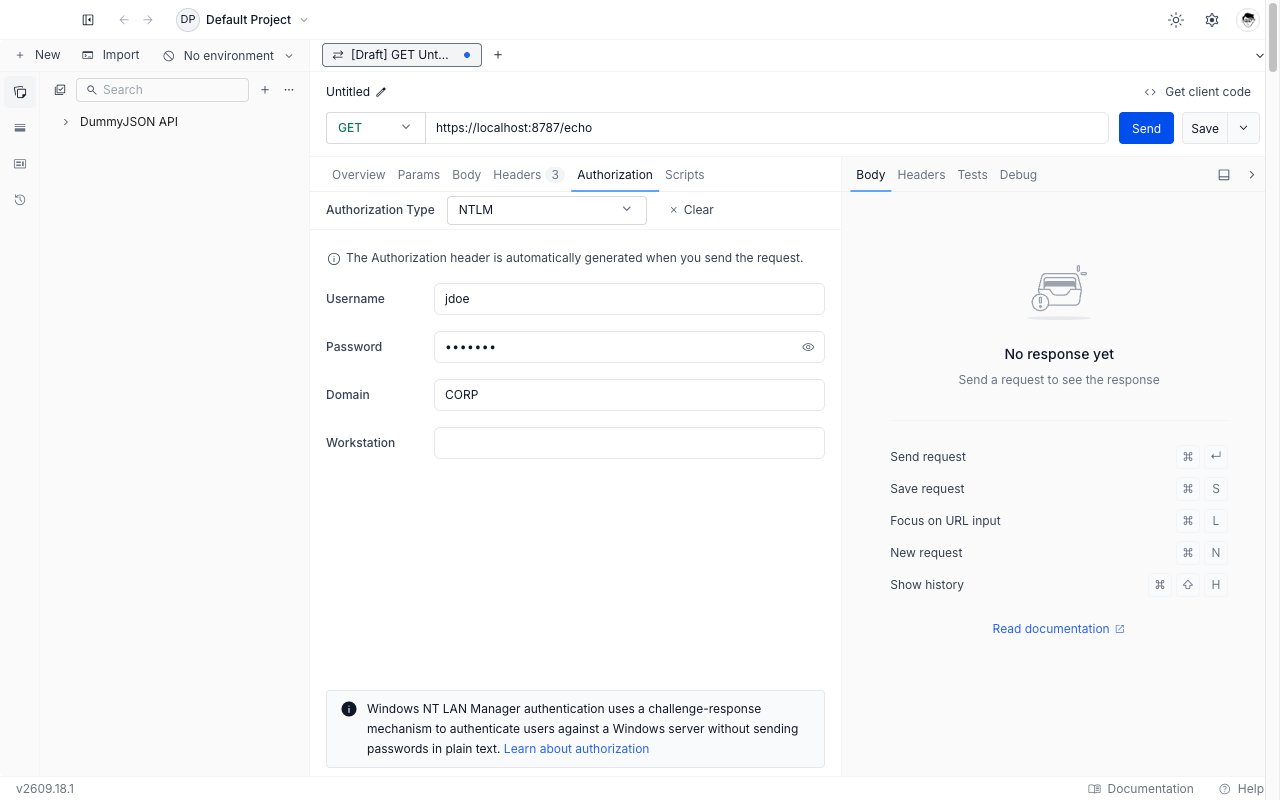
Open any request or collection in the desktop app, then go to the Authorization tab.
2
Select NTLM
Pick NTLM from the Authorization Type dropdown. The four NTLM fields appear below the dropdown.
3
Enter your domain credentials
Fill in Username and Password, then Domain if your account belongs to one. See the field reference below.
4
Send the request
Click Send. Requestly completes the three-message handshake and returns the authenticated response.
Field reference
All four fields accept Requestly variables and vault references.
Inherit NTLM from a collection
A domain usually fronts many endpoints, so NTLM is a good fit for collection-level auth. Set it once on the collection and leave every request inside on Inherit from parent. Requestly walks up from the request to the nearest ancestor that sets a concrete auth type. A request that picks its own auth type stops inheriting, and a collection or folder whose auth type is cleared or left unset stops the walk for everything below it.Troubleshooting
NTLM is missing or unselectable in the dropdown
NTLM is missing or unselectable in the dropdown
The web app cannot use NTLM. Open the same project in the desktop app. In the desktop app, NTLM is also unavailable while the execution target is the Cloud Agent, so switch the target back to your own machine.
The server returns 401 with correct credentials
The server returns 401 with correct credentials
Check how you split the account name.
DOMAIN\jdoe in Username with DOMAIN also in Domain sends the domain twice and fails. Use one or the other.The endpoint expects Kerberos or Negotiate
The endpoint expects Kerberos or Negotiate
Requestly signs with NTLMv2. A server configured for Kerberos or SPNEGO only will refuse the handshake. Ask your administrator whether the endpoint accepts NTLM fallback.
What’s Next?
Digest Auth
The other challenge-response scheme in the dropdown.
Vault
Keep domain credentials off the collection.
Authorization
Back to every auth type Requestly supports.